How to Pre-Populate Parameters to Avoid SQL Injection Attacks
This video is part of LearnItFirst's SQL Server 2008/R2 Reporting Services course. More information on this video and course is available here:
http://www.learnitfirst.com/Course162
In the previous video Scott talked about SQL Injections, which can create a lot of problems. In this video he will show you how to pre-populate Reporting Services parameters in order to avoid a SQL Injection attack.
Highlights from this video:
Implicitly declare parameter
Pre-populate parameter
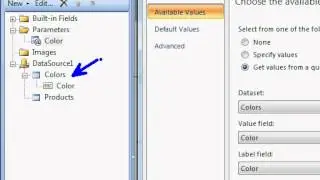
Continuing color example- drop down menu of color choices
Available values
Get values from a query
and much more...
На этой странице сайта вы можете посмотреть видео онлайн How to Pre-Populate Parameters to Avoid SQL Injection Attacks длительностью часов минут секунд в хорошем качестве, которое загрузил пользователь LearnItFirst.com 11 Февраль 2013, поделитесь ссылкой с друзьями и знакомыми, на youtube это видео уже посмотрели 2,203 раз и оно понравилось 1 зрителям. Приятного просмотра!